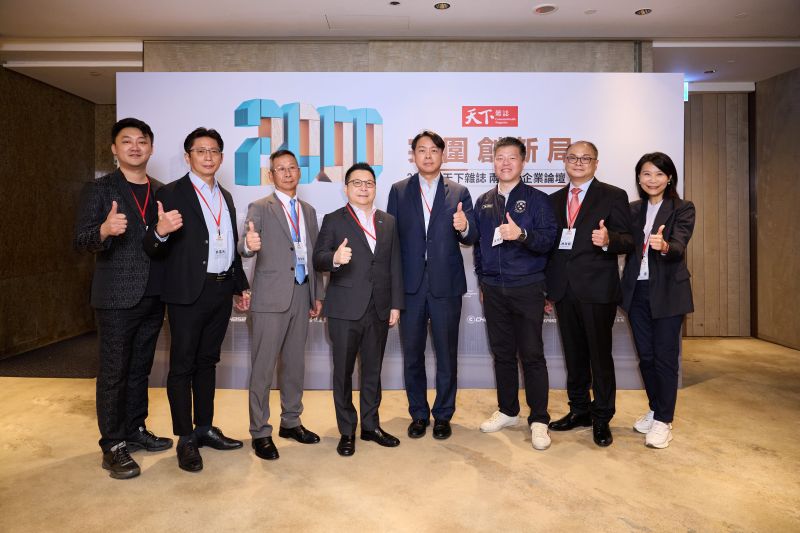
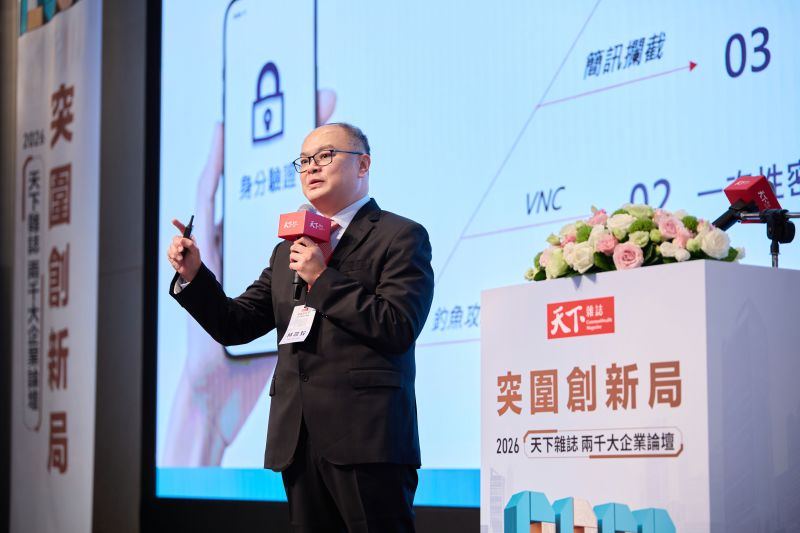
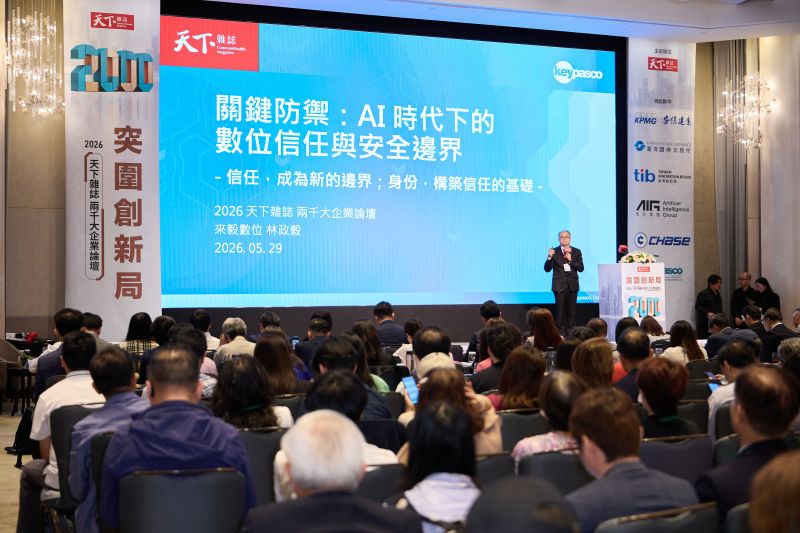
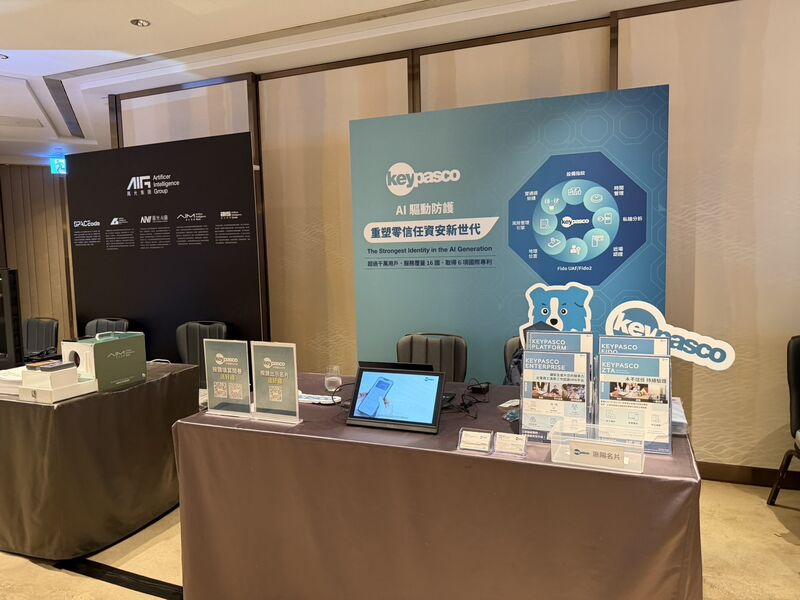
On May 29, 2026, our founder and chairman represented Lydsec Keypasco at CommonWealth Magazine’s 2000 Forum in Taipei. In a presentation on digital trust and security boundaries in the AI era, we explored a question that is becoming central to enterprise security: when AI participates in everyday operations, how do we know who is acting, what they are authorized to do, and whether each action can be trusted?
The forum took place at the Far Eastern hotel in Taipei. Our presentation focused on identity impersonation, uncontrolled permissions, and the difficulty of tracing responsibility, with three principles for building digital trust.
Location no longer defines trust
Cloud services, AI applications, and supply-chain relationships extend enterprise operations beyond the office and the internal network. Being inside a company network is no longer a sufficient basis for trust. We need to consider identity, the device, and the context of each access request.
This shifts the security boundary from a fixed network location to the trust decision surrounding each interaction. Consistent identity and permission management becomes essential across different working environments and connected services.
Trusted AI begins with trusted identities
People are no longer the only actors signing in, accessing information, or issuing instructions. AI agents and services connected through APIs also take part in enterprise workflows. Establishing who is acting is the starting point for trust.
We emphasized the need to consider identity, authorization, and accountability together. As organizations introduce AI into their workflows, they need a clear understanding of the actor and its authorized scope, so that digital trust can extend to new ways of working.
Trust is the result of continuous verification
Trust should not depend solely on a check made at sign-in. We highlighted a dynamic approach that combines identity, device, and contextual information, allowing verification to respond to changes in the environment and risk.
Through Keypasco multi-factor authentication and FIDO Passkey technology, we help organizations build passwordless security architectures. These authentication capabilities provide a foundation for digital trust and work alongside the organization’s permission management and operational processes.
A foundation for enterprise AI
AI creates new ways of working and new reasons to revisit established security boundaries. Moving from location to context, from sign-in to the identity behind each action, and from a single check to continuous verification were the central ideas we shared at the forum.
If you are planning MFA, passwordless authentication, or a Zero Trust architecture, contact our team to discuss a digital trust foundation suited to your environment.
Related information: Lydsec Keypasco’s forum recap and CommonWealth Magazine’s 2026 2000 Forum.